Boosting Cybersecurity ROI: 4 Essential Tech Upgrades for US Businesses in Q3 2026 (FINANCIAL IMPACT)
In an increasingly interconnected digital landscape, the question for US businesses is no longer if they will face a cyberattack, but when. The sheer volume and sophistication of cyber threats continue to escalate, making robust cybersecurity not just a necessity, but a strategic imperative. However, in today’s economic climate, every investment must demonstrate a clear and tangible return on investment (ROI). This article delves into four essential tech upgrades that US businesses should consider implementing in Q3 2026 to significantly boost their cybersecurity ROI upgrades, ensuring not only enhanced protection but also a positive financial impact.
Understanding the financial implications of cybersecurity is paramount. A data breach can lead to devastating financial losses, including regulatory fines, legal fees, reputational damage, lost productivity, and the cost of remediation. According to various industry reports, the average cost of a data breach continues to climb, making proactive investment in cybersecurity a far more cost-effective strategy than reactive crisis management. By focusing on smart, strategic upgrades, businesses can transform their cybersecurity expenditures from a perceived cost center into a value-generating asset.
This comprehensive guide will outline key technological advancements that offer superior protection while also delivering measurable financial benefits. We will explore how these upgrades contribute to reduced operational costs, improved compliance posture, enhanced business continuity, and ultimately, a stronger bottom line. Prepare to optimize your cybersecurity strategy for Q3 2026 and beyond.
The Evolving Threat Landscape and the Need for Strategic Investment
The digital threat landscape is a dynamic and ever-evolving battleground. Cybercriminals are constantly developing new tactics, from advanced persistent threats (APTs) and sophisticated ransomware to elaborate phishing schemes and supply chain attacks. For US businesses, this means that static, traditional cybersecurity measures are no longer sufficient. Continuous adaptation and strategic investment in cutting-edge technologies are crucial for maintaining a resilient defense.
The financial impact of cyberattacks extends far beyond immediate remediation costs. Reputational damage can lead to customer churn, loss of market share, and difficulty attracting new talent. Regulatory fines, particularly under frameworks like GDPR, CCPA, and upcoming state-specific privacy laws, can be crippling. Moreover, the disruption to business operations can halt productivity, delay projects, and impact revenue generation. Therefore, investing in cybersecurity ROI upgrades is not merely about preventing attacks; it’s about safeguarding the entire business ecosystem.
In Q3 2026, businesses must look beyond basic antivirus and firewalls. The focus needs to shift towards proactive, intelligent, and integrated security solutions that can anticipate, detect, and respond to threats with speed and precision. The upgrades discussed below are selected for their proven ability to enhance security posture while also offering significant returns through efficiency gains, risk reduction, and improved compliance.
1. Advanced Threat Detection and Prevention Systems (ATDP)
Traditional signature-based antivirus solutions are increasingly ineffective against polymorphic malware and zero-day exploits. Advanced Threat Detection and Prevention (ATDP) systems, which include technologies like Endpoint Detection and Response (EDR), Extended Detection and Response (XDR), and Security Information and Event Management (SIEM) with User and Entity Behavior Analytics (UEBA), represent a significant leap forward in proactive cybersecurity.
What are ATDP Systems?
ATDP systems leverage artificial intelligence (AI) and machine learning (ML) to analyze vast amounts of data from various sources across an organization’s IT environment. They identify anomalous behaviors, detect sophisticated threats that bypass traditional defenses, and provide comprehensive visibility into security incidents. EDR focuses on endpoints (laptops, servers), XDR extends this to cover networks, cloud environments, and applications, while SIEM aggregates and analyzes security event data, often enhanced by UEBA to detect insider threats and compromised accounts.
Financial Impact and ROI:
- Reduced Breach Costs: By detecting and neutralizing threats earlier, ATDP systems significantly reduce the mean time to detect (MTTD) and mean time to respond (MTTR) to incidents. This minimizes the scope and impact of breaches, leading to substantial savings in remediation costs, legal fees, and regulatory fines.
- Proactive Risk Mitigation: ATDP’s predictive capabilities help organizations identify vulnerabilities and potential attack vectors before they can be exploited. This proactive stance reduces the likelihood of successful attacks, thereby preventing costly disruptions and data loss.
- Operational Efficiency: Automated threat detection and response capabilities reduce the workload on security teams, allowing them to focus on higher-level strategic tasks. This optimization of human resources translates into operational cost savings.
- Improved Compliance: Enhanced visibility and logging capabilities provided by ATDP systems simplify compliance with various regulatory frameworks, reducing the risk of non-compliance penalties.
- Enhanced Business Continuity: By preventing widespread disruptions caused by cyberattacks, ATDP systems ensure continuous business operations, safeguarding revenue streams and maintaining productivity.
Implementing an ATDP solution in Q3 2026 is a critical step for US businesses looking to move beyond reactive security and embrace a more resilient, intelligent defense strategy that directly contributes to their cybersecurity ROI upgrades.
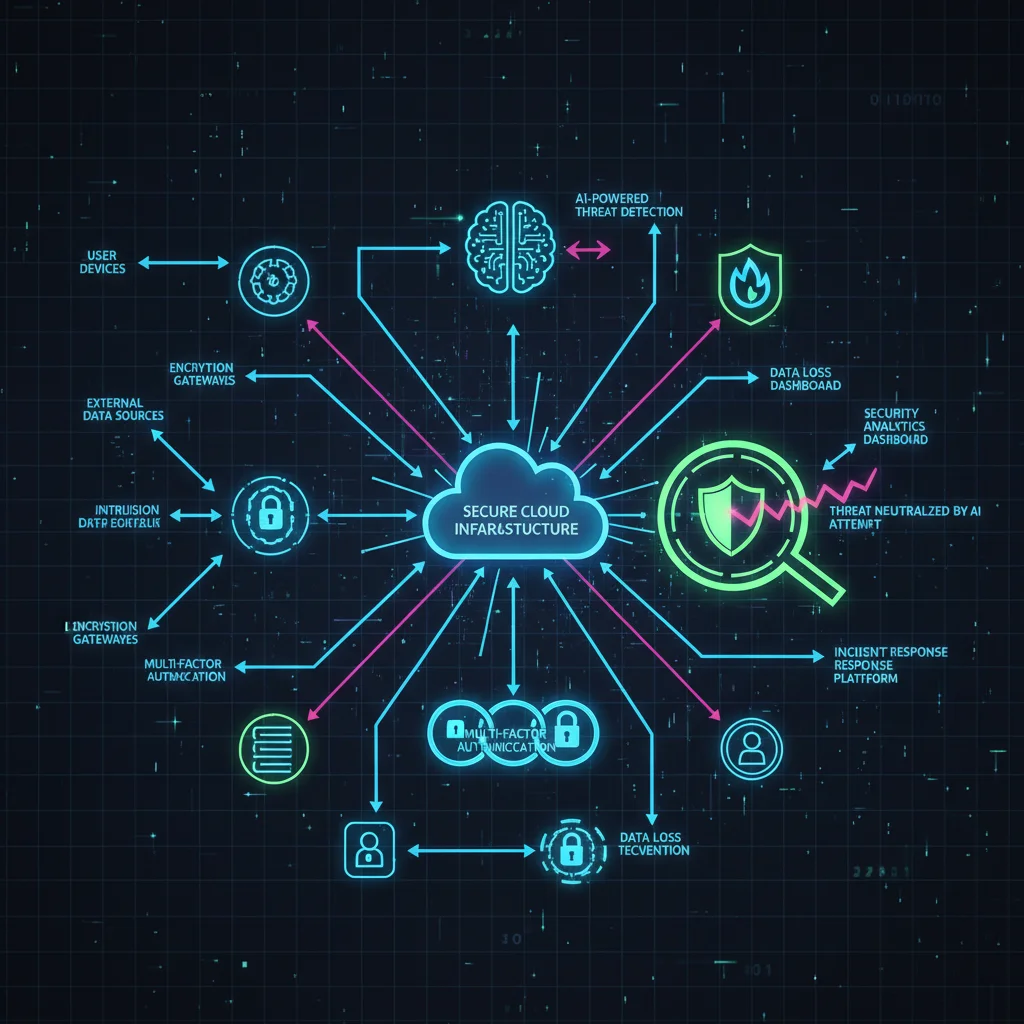
2. Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platforms (CWPP)
As more US businesses migrate to cloud environments, securing these distributed and dynamic infrastructures becomes paramount. Traditional on-premise security tools are often inadequate for cloud-native applications and services. Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platforms (CWPP) are essential for ensuring security and compliance in the cloud.
What are CSPM and CWPP?
CSPM solutions continuously monitor cloud environments (AWS, Azure, Google Cloud) to identify misconfigurations, compliance violations, and security risks. They provide visibility into cloud assets, enforce security policies, and automate remediation of common vulnerabilities. Misconfigurations are a leading cause of cloud breaches, and CSPM helps address this proactively.
CWPP solutions focus on securing individual workloads (virtual machines, containers, serverless functions) running in the cloud. They offer capabilities like vulnerability management, runtime protection, host-based firewalls, and application control to protect against exploits and unauthorized access at the workload level.
Financial Impact and ROI:
- Reduced Cloud Breach Costs: By preventing misconfigurations and protecting cloud workloads, CSPM and CWPP drastically reduce the risk and cost associated with cloud-based data breaches, which can be particularly expensive due to the scale of data often stored in the cloud.
- Automated Compliance: Both CSPM and CWPP automate the enforcement of security policies and compliance standards (e.g., NIST, PCI DSS, HIPAA) across cloud environments. This reduces manual effort, minimizes audit preparation time, and lowers the risk of non-compliance fines.
- Optimized Cloud Spending: By identifying unused or misconfigured cloud resources that pose security risks, CSPM can also indirectly help optimize cloud spending by highlighting inefficient resource allocation.
- Faster Development Cycles: Integrating CSPM and CWPP into CI/CD pipelines (DevSecOps) allows developers to build secure applications from the outset, reducing costly rework and delays caused by security vulnerabilities discovered later in the development cycle.
- Enhanced Operational Efficiency: Centralized visibility and automated remediation provided by these platforms streamline cloud security operations, freeing up security teams to focus on more complex threats.
For any US business leveraging cloud infrastructure, investing in robust CSPM and CWPP solutions in Q3 2026 is a non-negotiable step towards achieving significant cybersecurity ROI upgrades and ensuring the integrity of their cloud assets.
3. Zero Trust Network Access (ZTNA)
The traditional perimeter-based security model, where everything inside the network is trusted and everything outside is not, is obsolete in today’s hybrid work environments and cloud-centric architectures. Zero Trust Network Access (ZTNA) is a modern security framework that fundamentally shifts this paradigm, adopting a ‘never trust, always verify’ approach.
What is ZTNA?
ZTNA operates on the principle that no user or device, whether inside or outside the network, should be implicitly trusted. Access to resources is granted on a least-privilege basis, after continuous verification of user identity, device posture, and context. Instead of granting broad network access, ZTNA establishes secure, individualized connections to specific applications and data, isolating users from the broader network.
Financial Impact and ROI:
- Reduced Risk of Lateral Movement: ZTNA significantly limits an attacker’s ability to move laterally within a network once a breach occurs. By segmenting access, it contains the blast radius of a successful attack, drastically reducing potential damage and remediation costs.
- Enhanced Remote Work Security: With the proliferation of remote and hybrid work models, ZTNA provides a far more secure alternative to traditional VPNs. It ensures that remote users have secure, granular access to only the resources they need, without exposing the entire corporate network, thereby preventing costly breaches originating from remote endpoints.
- Simplified Security Management: ZTNA centralizes access control and policy enforcement, simplifying security management across diverse environments (on-premise, cloud, remote). This reduces administrative overhead and potential for human error.
- Improved Compliance Posture: The granular access control and continuous verification inherent in ZTNA align well with various compliance requirements for data access and protection, making audits easier and reducing compliance risks.
- Cost Savings from VPN Reduction: While ZTNA isn’t a direct replacement for all VPN use cases, it can significantly reduce reliance on traditional VPN infrastructure, potentially leading to cost savings in licensing, maintenance, and bandwidth.
Adopting a ZTNA model in Q3 2026 is a strategic move for US businesses seeking to fortify their security posture against increasingly sophisticated threats, particularly those targeting remote access and cloud resources. This investment will yield substantial cybersecurity ROI upgrades by minimizing breach impact and streamlining access management.
4. Security Awareness Training and Phishing Simulation Platforms
Technology alone cannot fully protect an organization. The human element remains the weakest link in the cybersecurity chain. Employees are often the primary targets for cybercriminals through social engineering tactics like phishing, spear-phishing, and pretexting. Comprehensive and continuous security awareness training, coupled with realistic phishing simulations, is a vital component of a holistic cybersecurity strategy.
What are Security Awareness Training and Phishing Simulation Platforms?
These platforms provide engaging, interactive training modules that educate employees on various cybersecurity threats, best practices, and organizational policies. Topics typically include identifying phishing emails, strong password creation, safe browsing habits, data handling, and incident reporting. Phishing simulation tools send realistic fake phishing emails to employees to test their vigilance and identify individuals who may need additional training. These platforms track performance, provide detailed reports, and offer targeted remedial training.
Financial Impact and ROI:
- Reduced Risk of Human-Caused Breaches: By empowering employees to recognize and report threats, these platforms significantly reduce the likelihood of successful attacks that exploit human error. This directly translates to avoiding the enormous financial costs associated with data breaches.
- Lower Incident Response Costs: A well-trained workforce is less likely to fall victim to sophisticated attacks, which means fewer security incidents for the IT and security teams to investigate and remediate, leading to direct savings in operational costs.
- Improved Compliance and Reduced Fines: Many regulatory frameworks (e.g., HIPAA, PCI DSS) mandate regular security awareness training. Implementing a robust program ensures compliance, reducing the risk of hefty fines and legal repercussions.
- Enhanced Corporate Culture of Security: A security-aware workforce contributes to a stronger overall security posture. Employees become an active part of the defense, acting as an additional layer of protection. This proactive culture can lead to long-term cost savings by embedding security into daily operations.
- Protection Against Ransomware: Many ransomware attacks begin with a phishing email. Effective training can significantly reduce the chances of an employee clicking on a malicious link or opening an infected attachment, thereby preventing potentially catastrophic and expensive ransomware incidents.
For US businesses, investing in a leading security awareness training and phishing simulation platform in Q3 2026 offers an exceptionally high cybersecurity ROI upgrades. It transforms employees from potential vulnerabilities into a formidable line of defense, safeguarding assets and reputation.
Measuring and Maximizing Cybersecurity ROI
To truly understand the value of these cybersecurity investments, US businesses must establish clear metrics for measuring ROI. This goes beyond simply tracking the absence of breaches. Key performance indicators (KPIs) can include:
- Mean Time To Detect (MTTD) and Mean Time To Respond (MTTR): Shorter times indicate more efficient security operations and reduced breach impact.
- Number of Security Incidents/Breaches Prevented: Quantifying averted costs is crucial.
- Compliance Audit Success Rates: Demonstrates reduced risk of fines.
- Employee Phishing Click Rates: Shows improvement in human defense.
- Cost Savings from Automation: Quantifies efficiency gains.
- Insurance Premium Reductions: Strong cybersecurity can lead to lower cyber insurance premiums.
- Reputational Impact: While harder to quantify, maintaining customer trust is invaluable.
Maximizing ROI also involves continuous evaluation and optimization. Regularly review the effectiveness of implemented solutions, stay abreast of emerging threats, and adapt your security strategy accordingly. Integrating these upgrades into a broader cybersecurity framework, such as a Security Operations Center (SOC) or managed security services, can further enhance their impact and efficiency.
Conclusion: A Proactive Approach to Financial Security
For US businesses navigating the complexities of the digital age, cybersecurity is no longer an optional expense but a strategic investment that directly impacts financial health and long-term sustainability. The four essential tech upgrades discussed – Advanced Threat Detection and Prevention Systems, Cloud Security Posture Management and Cloud Workload Protection Platforms, Zero Trust Network Access, and Security Awareness Training with Phishing Simulations – represent critical areas for investment in Q3 2026.
By prioritizing these cybersecurity ROI upgrades, organizations can build a resilient defense against evolving threats, reduce the catastrophic costs associated with cyberattacks, ensure regulatory compliance, and foster a culture of security. The financial impact of these investments extends far beyond mere protection; it encompasses operational efficiency, business continuity, and enhanced stakeholder trust, ultimately contributing to a stronger, more secure, and more profitable future.
The time to act is now. Proactive investment in intelligent, integrated cybersecurity solutions will not only safeguard your assets but also empower your business to thrive securely in the digital economy of Q3 2026 and beyond.
Related Posts: